See who can reach cluster-admin — and which CVE to fix first.
Attack paths, image CVEs, misconfigurations and compliance scorecards, ranked in the same queue as reliability and upgrade risk. The agent that finds them is read-only and never reads a secret value.
one helm install · get, list, watch only · first findings in minutes
Overview
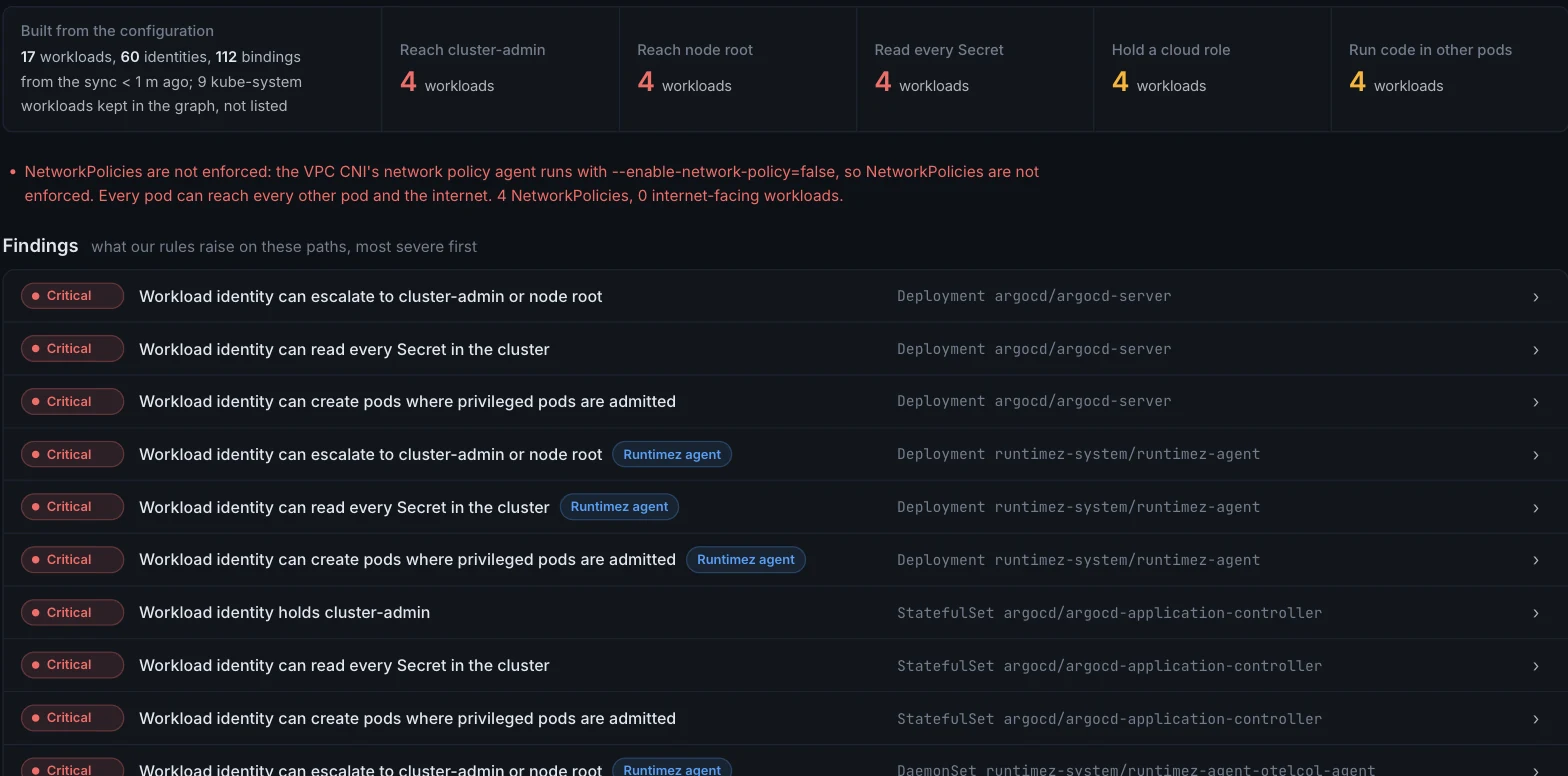
Security findings are only useful when they are ranked. Runtimez builds the graph of identities, bindings and workloads, scans every running image inside the cluster, and feeds the results into the same risk score as reliability and upgrades — so the CVE on the workload that also blocks your upgrade comes first.
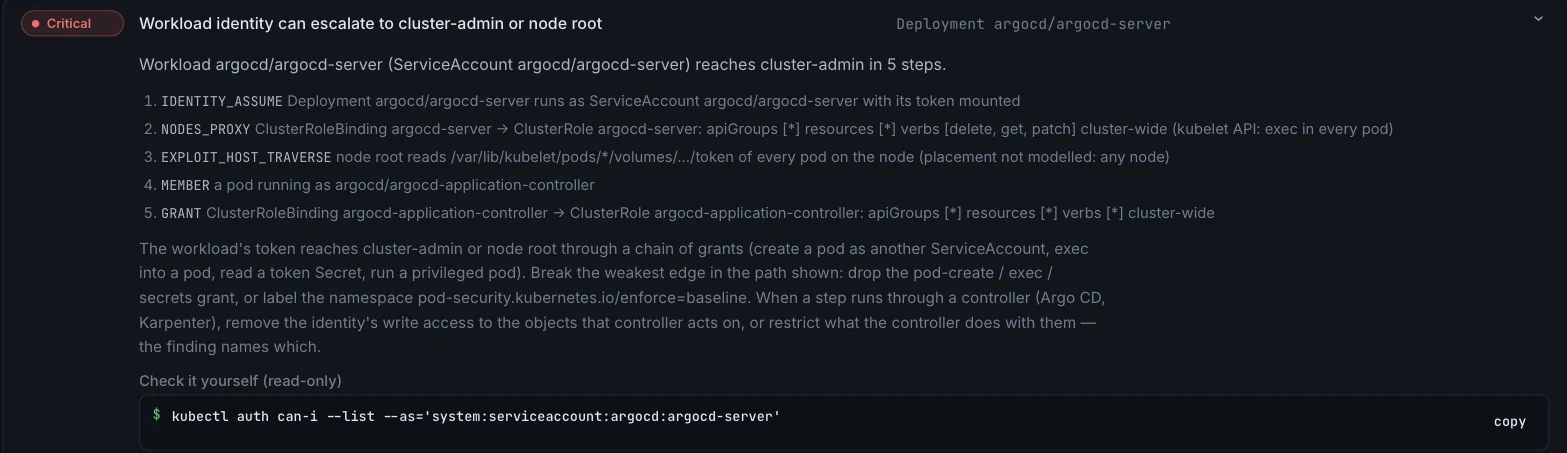
Every step from a workload to cluster-admin
18 rules over RBAC bindings, ServiceAccount tokens, pod escalation and cloud identity.
- The full chain, step by step: identity assumed, the binding that grants it, the host path it traverses.
- The weakest edge to break, and what to change when a step runs through a controller like Argo CD or Karpenter.
- A read-only
kubectl auth can-icommand to check the path yourself.
Every running image, scanned where it runs
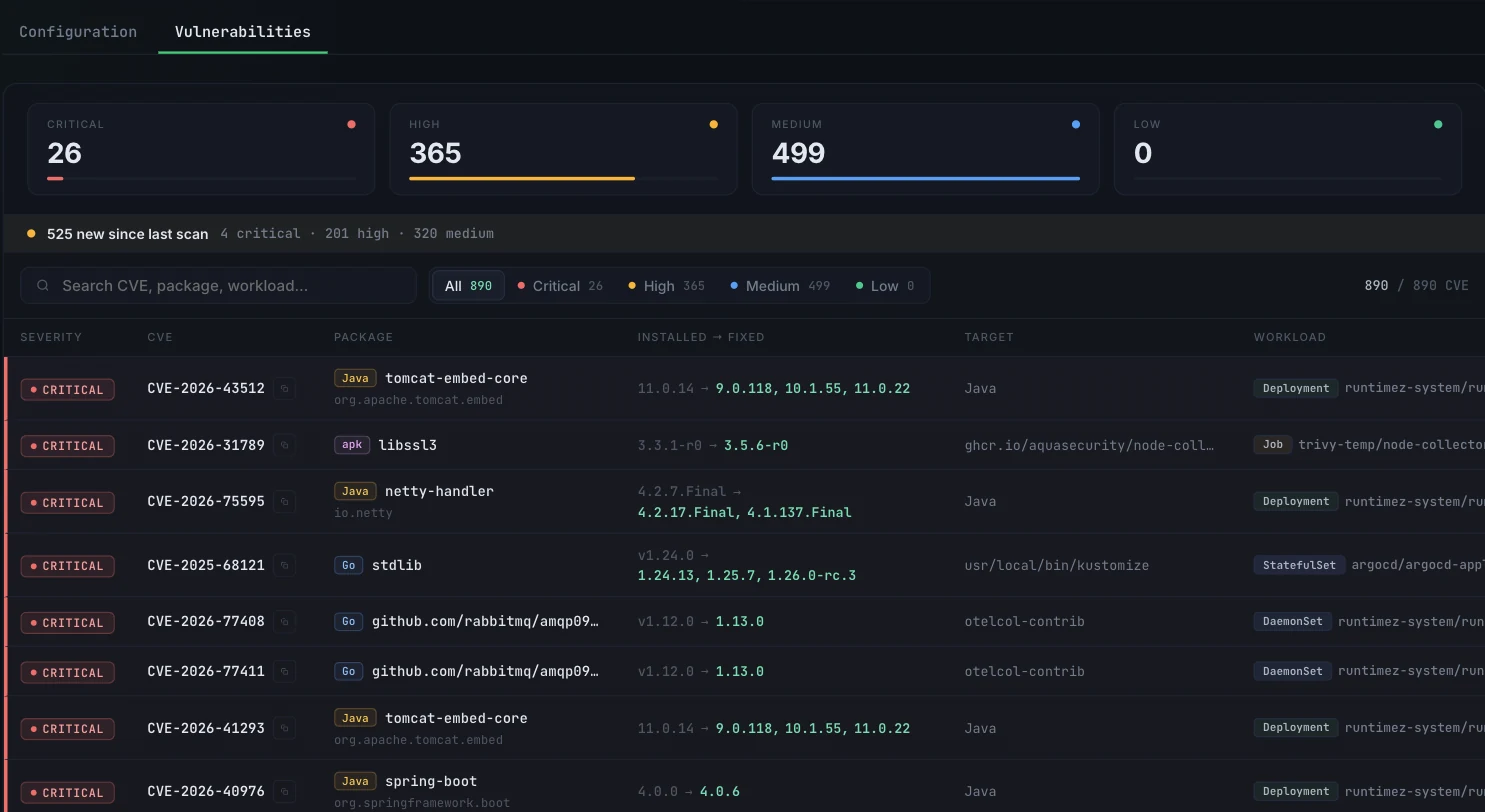
The scanner runs as an ephemeral Job inside your cluster. Images and pull secrets never leave.
- CVE, package, installed and fixed version, target and the workload that runs it.
- New since the last scan, by severity.
- CVE load feeds the workload risk score, so security and reliability share one ranking.
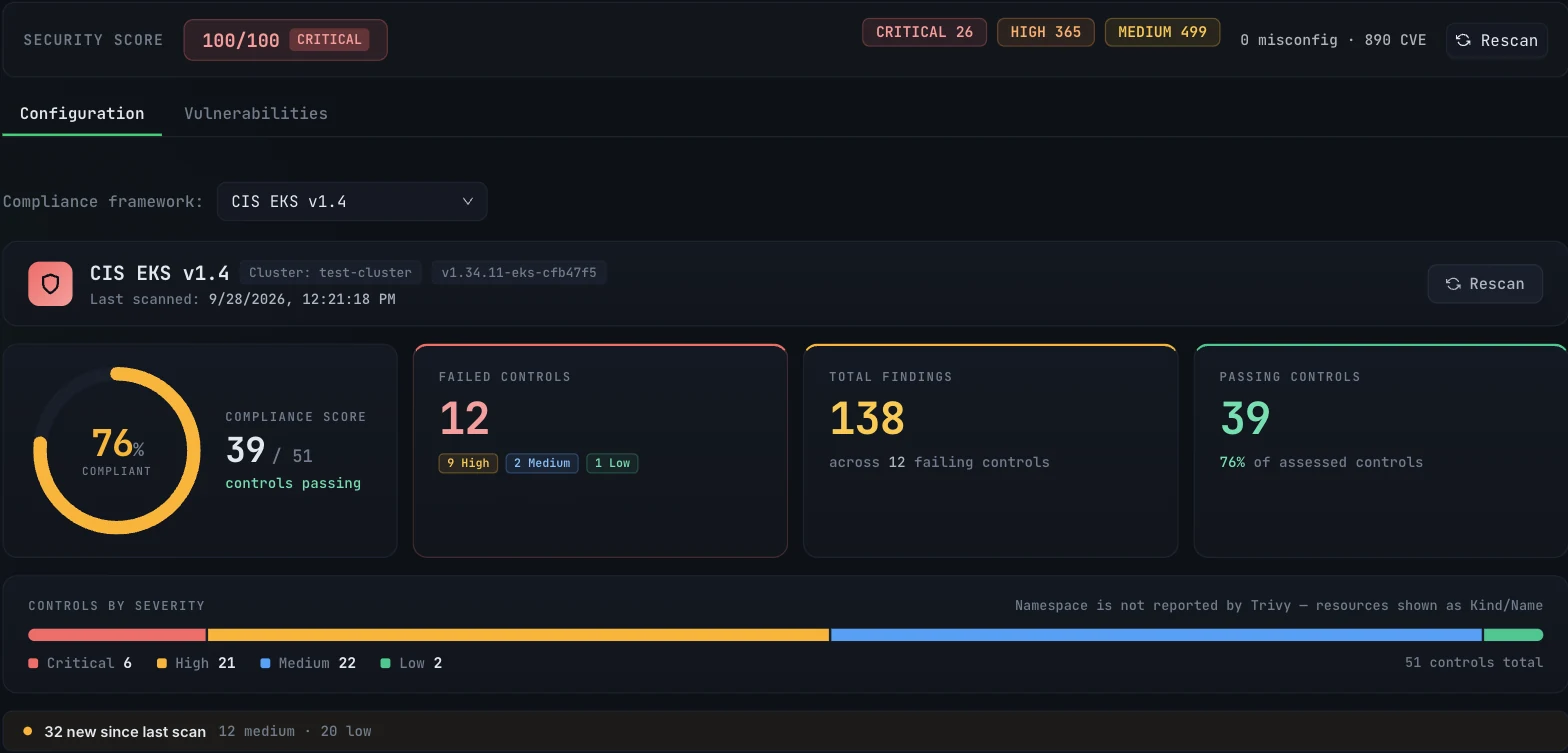
CIS and NSA scorecards per cluster
Pass or fail per control, with the failing resources named.
- CIS Kubernetes, CIS EKS and NSA frameworks.
- Failed controls by severity and what is new since the last scan.
- Rescan on demand and work from a prioritized remediation drawer.
One ranking for security and reliability
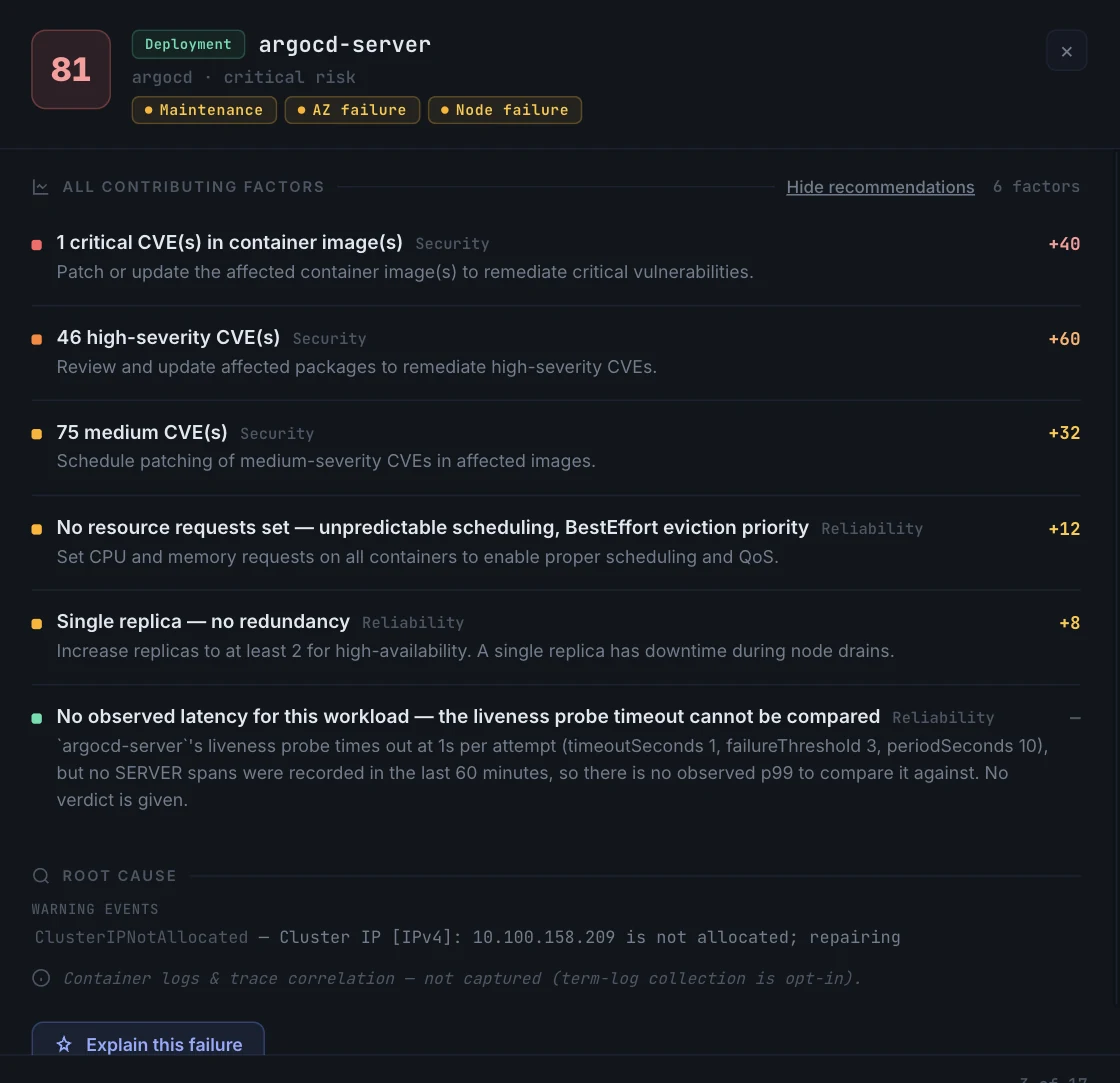
A critical CVE on the workload that also blocks your upgrade is ranked first, because one change clears both.
- CVE counts, missing requests and single replicas add up in one score per workload.
- Each factor shows how much it moved the score.
- The Runtimez agent's own findings are tagged as expected, with the chart value that removes each.
More in Kubernetes Security
Everything else that ships in this product today.
Read-only RBAC
Only get, list and watch. No mutating verbs, no kubeconfig handover, no inbound access. Uninstall is one command.
Secret names only
The inventory records that a secret exists. Values are never read or transmitted.
Misconfiguration posture
Privileged containers, running as root, hostPath mounts and missing security context add up to a posture score.
Unified score and fleet ranking
One security number per cluster, with the fleet ordered by criticality.
Multi-tenant with roles
Everything is org-scoped, with Owner, Admin, Platform Engineer, Developer and Viewer roles.
Redaction on every AI path
Evidence is scrubbed of secrets before it reaches any model.
How it compares
They rank CVEs by severity. Runtimez ranks them by which fix also unblocks your upgrade.
Where does image scanning run?
Inside your cluster, as an ephemeral Job. Images and pull secrets never leave the cluster; Runtimez receives findings only.
Does Runtimez read my secrets?
No. It records that a secret exists — its name — and never reads or transmits the value.
Which compliance frameworks are supported?
CIS Kubernetes, CIS EKS and NSA hardening guidance, with pass or fail per control.
Why does the Runtimez agent appear in attack paths?
Because any read-all identity is worth knowing about. Its findings are tagged as expected, with the Helm chart value that removes each one.
Related reading
One agent, the rest of the platform
Every product runs off the same read-only sweep and feeds the same ranked queue.
See it on your own cluster in under an hour.
Free for your first cluster. Read-only by default. Uninstall is one helm command.